Node.js Gets a Security Patch; Cat Engineers Convene an Emergency Tunnel Inspection
After Node.js published security releases across three release lines, the fictional Feline Tunnel Authority launches a careful patch-and-inspection drill.
Satire notice: This is fictional cat-world satire inspired by real software news. The feline characters, dialogue and events below are invented.
At 9:02 yesterday morning, the Department of Naps and Networked Things declared the Great Tunnel Secure—then immediately called an emergency meeting to discuss whether the tunnel had, in fact, been inspected from the inside.
The review began after the Node.js project published security updates for its 26.x, 24.x and 22.x lines on October 21. The real release notes describe several fixes, including high-severity issues involving DNS input handling, TLS address validation and a Brotli decoder. In the cat republic, this news was translated as: “The tunnel has a few holes, and one of them may be larger than the treat budget.”
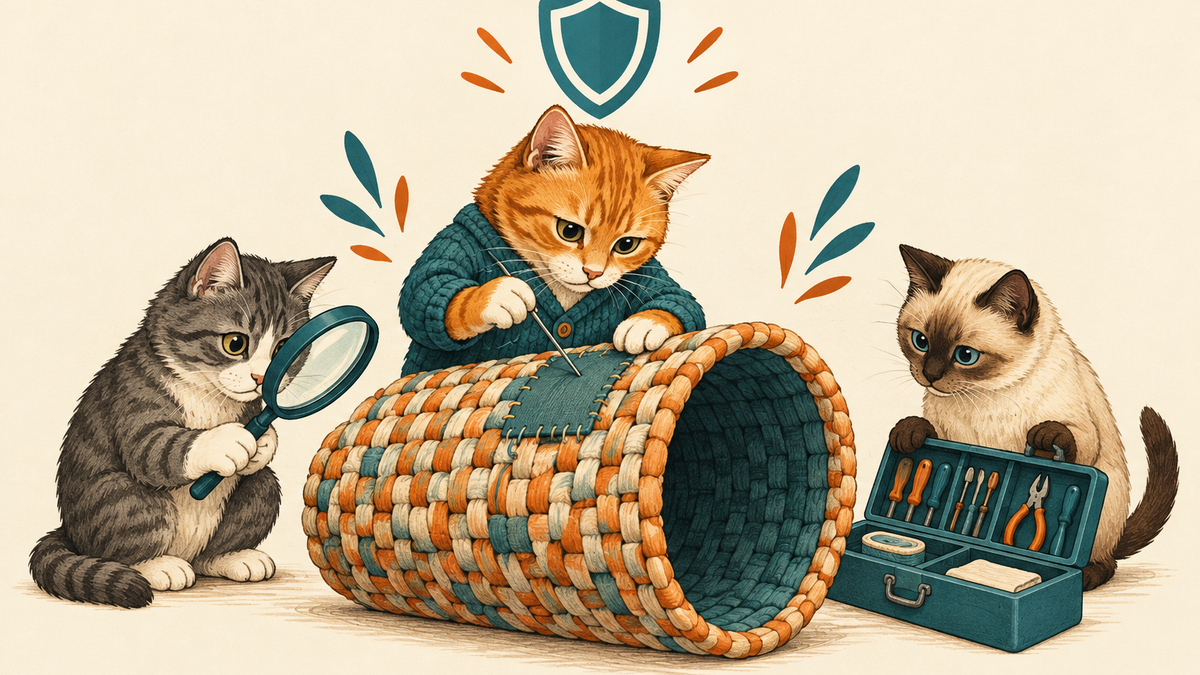
Chief Patch Officer Marmalade arrived carrying a spool of teal yarn and a clipboard. “We will not panic,” she announced, while putting on three safety helmets. “We will calmly update every tunnel, test the doors, and ask why the door was built out of compressed crumbs.”
Her team’s first challenge was the compatibility maze. The senior cats insisted the old tunnel still worked because they had napped in it last Tuesday. The junior cats pointed out that “worked once, while nobody was watching” was not a security policy. A tabby intern proposed a controlled rollout: patch one section, inspect it, then proceed. The proposal passed unanimously after the intern placed a cardboard box over the conference-room projector.
Meanwhile, the Department’s official update guide advised residents to install the appropriate release for their line. Marmalade’s fictional bulletin put it more plainly: “If your tunnel is running an affected build, please stop storing passwords, fish recipes, and highly sensitive sunbeam coordinates inside it until maintenance is complete.” The bulletin also clarified that ordinary cats should follow the software project’s actual guidance—not a whiskered parody on the internet.
By lunchtime, the inspectors had discovered that the tunnel’s emergency exit opened into a second tunnel, which opened into a cupboard, which contained a suspiciously comfortable basket. Marmalade ordered the basket quarantined pending review. The team filed three findings: patch promptly, keep dependencies current, and never let the cat who owns the basket certify the basket.
At a brief press conference, Marmalade declared the operation a success. Asked whether the tunnels were now perfectly safe, she replied, “No system deserves that adjective. We have applied the available fixes, checked our work, and scheduled another inspection after snack time.” The room applauded—except the intern, who was busy checking the version number.
In the real world, Node.js announced security releases on October 21, 2026 for the 26.x, 24.x and 22.x release lines. The project lists multiple vulnerabilities and recommends using an up-to-date supported release. This article’s cat officials, tunnel metaphor and dialogue are fictional.
The real news behind the joke
The Node.js project published security updates for versions 26.x, 24.x and 22.x on October 21, 2026. Its advisory describes multiple issues, including high-severity vulnerabilities and dependency updates. The Node.js 22.23.4 release notes independently confirm the date and list security fixes. Check the official guidance and update the relevant supported release line.
Sources
- Node.js Project: October 21, 2026 security releases
- Node.js 22.23.4 (LTS) release notes
- Node.js v22.23.4 GitHub release
Illustration generated with AI.